Security & compliance
How Milemarker protects your firm's data
Wealth management firms trust Milemarker with client and account data. Here you'll find our independent audit, the safeguards we commit to, our policies, insurance and subprocessors, and the people accountable for them.
Independent assurance
SOC 2 Type II
Report availableSecurity trust services criteria · Audit period 2 June 2025 to 1 June 2026 · Examined by Johanson Group LLP
Documents
These are shared with clients, prospective clients and their advisers under our Confidentiality Agreement. Request access below. Once approved, you'll get an email to set up a sign-in, and you can download them from this page. Already approved? Sign in.
-
SOC 2 Type II report
Our latest independent audit of our security controls
Available after approval -
Security policies
Every published policy, bound as one PDF
Available after approval -
Certificate of insurance: cyber and technology E&O
Our current certificate from the insurer
Available after approval -
Certificate of insurance: general liability
Our current certificate from the insurer
Available after approval
Request access
Security leadership
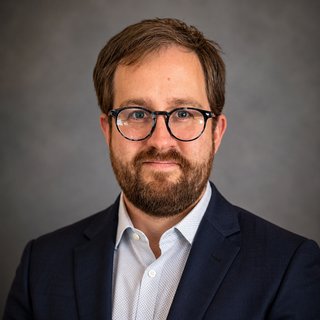
Kevin Farrow
Chief Information Security Officer
Kevin leads Milemarker's security and compliance program: the policies on this page, our annual SOC 2 Type II examination, penetration testing, and the security reviews we complete with clients and prospective clients.
He is a penetration tester and application security engineer by background, and has held the OffSec Certified Professional (OSCP) credential since 2019.
Security controls
The controls behind the answers most security questionnaires ask for. Once you sign in, each links to its source: the Service Security Standards, which are our binding commitments and govern if anything here differs (reading them requires a documentation account), or our published security policies.
Data protection
6 controls
Endpoint security
5 controls
Identity and access
5 controls
Secure development
5 controls
Monitoring and incident response
5 controls
People
4 controls
Business continuity
3 controls
AI and vendors
4 controls
Sign in or request access to see these controls.
Security policies
Milemarker's security program runs on 34 written policies across 7 areas, reviewed at least annually and acknowledged by every employee and contractor. Copies are available to clients and approved reviewers on request.
Governance and risk
8 policies
Access and identity
4 policies
Data protection and privacy
7 policies
Engineering and operations
6 policies
Resilience and response
2 policies
People and vendors
3 policies
Customers and data providers
4 policies
Sign in or request access to see the policy titles.
Subprocessors
Third parties that store, process or can access data on Milemarker's behalf. Each is bound by written confidentiality and security obligations, and we notify clients in writing before adding or replacing a core subprocessor that stores or processes client data. Systems your firm chooses to connect, such as your own AI assistants or BI tools, are not Milemarker subprocessors.
| Subprocessor |
|---|
 Amazon Web Services |
| Anthropic |
 ClickUp |
 Comp AI |
| Google |
 Help Scout |
 HubSpot |
 Slack |
 Snowflake |
Each subprocessor's purpose and the terms it's bound by are shared once you sign in or request access.
Security questionnaires
Send us your firm's questionnaire (SIG, CAIQ, VSA or your own) and our security team will complete it and email it back to you. Tell us when you need it and we'll plan around that date.
Report a security issue
To report a vulnerability or a suspected security incident, or to ask for a copy of a single policy, email security@milemarker.co.
Controls, policies, subprocessors and insurance last reviewed 5 October 2026.